
Email & Internet Rules Every Small Business Needs
Clear email and internet rules protect your small business from legal risk, security threats, and workplace problems.
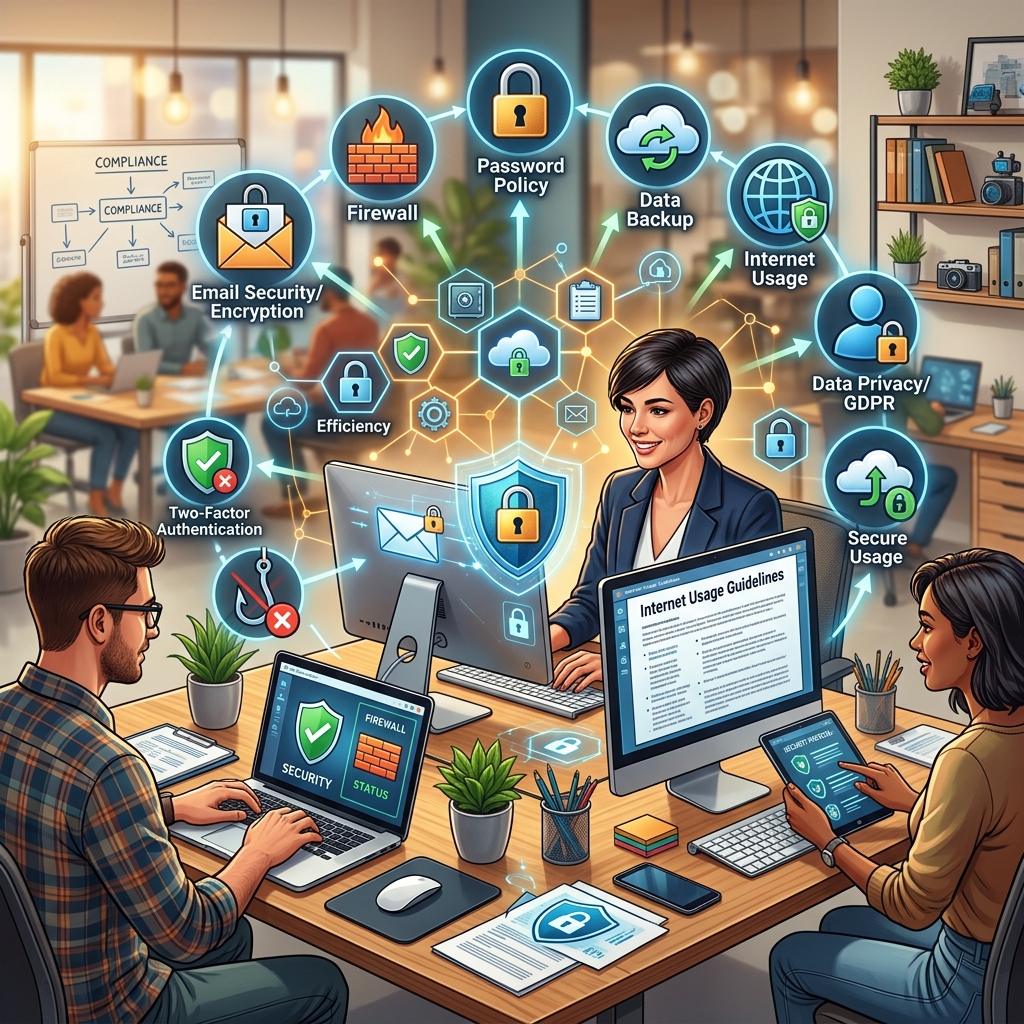
For many small businesses, email, web tools, and cloud platforms are as essential as phones and desks. Yet a surprising number of employers still rely on informal understandings instead of written rules for technology use. A clear, legally sound email and internet policy can reduce your risk of lawsuits, data breaches, and workplace conflict while giving employees practical guidance on what is expected of them.
This article explains why your business needs a documented policy, what it should cover, and how to roll it out effectively. It is inspired by legal guidance on workplace technology but presents an original, practical framework for owners and managers.
Why Small Businesses Need Written Email & Internet Rules
Even in a small team, informal norms are not enough. Once employees are sending and receiving work emails, accessing cloud systems, and browsing the web on company time, you are exposed to legal, security, and reputation risks that a written policy can help control.
Key reasons to adopt a formal policy
- Legal protection: A written policy clarifies that company systems are for business use, defines what is prohibited, and helps demonstrate that you took reasonable steps to prevent harassment, misuse of data, and unlawful activity.
- Security and data protection: Employees often handle sensitive customer and employee information. A policy can require safe handling of personal data, strong passwords, and caution with links and attachments, supporting cybersecurity best practices and privacy obligations.
- Productivity and focus: Clear limits on non-work browsing, streaming, and social media reduce distractions during work hours and help keep company systems performing well.
- Clarity and consistency: A documented standard avoids misunderstandings like “I didn’t realize that wasn’t allowed” and ensures supervisors apply rules fairly.
- Support for monitoring and retention: If you review work emails or log web activity, a policy alerts employees to that practice and explains why, reducing feelings of intrusion when monitoring is needed.
Common risks small businesses face
- Harassing or discriminatory messages: Workplace email and chat tools can be used for offensive jokes or bullying, leading to potential claims under anti-discrimination and harassment laws when employers fail to address them.
- Data breaches and phishing: Attackers often use email to trick employees into sharing login credentials, sending payments, or opening malware. Policies and training help employees recognize and report suspicious messages before damage occurs.
- Unlawful content sharing: Employees might download pirated software, share copyrighted materials, or forward confidential information without permission. The business may be held responsible if policies are absent or not enforced.
- Reputation damage: A poorly worded message sent from a company address or an inappropriate online post can harm customer trust and brand image.
Core Elements of a Strong Email & Internet Policy
A good policy is tailored to your business but usually covers the same core topics: acceptable use, security, privacy, and consequences. The goal is not to micromanage employees, but to set clear boundaries that protect everyone.
1. Acceptable and Unacceptable Use
Your policy should begin by defining how company systems may and may not be used. This section is the foundation for later enforcement and training.
- Business purpose: State that company email accounts, messaging tools, and internet access are primarily for business-related communications and tasks.
- Limited personal use: You may allow minor personal use (such as checking a personal email account during breaks) so long as it does not interfere with work, violate laws, or consume excessive resources.
- Prohibited content and activity: Clearly forbid using company systems to send or access content that is harassing, discriminatory, defamatory, sexually explicit, threatening, or otherwise unlawful. Also prohibit fraud, hacking, or use of unlicensed software.
- Professional tone: Require employees to maintain a professional, courteous tone when communicating with customers, partners, and colleagues.
| Acceptable Uses | Unacceptable Uses |
|---|---|
| Customer support, quotes, project updates | Harassing, discriminatory or sexually explicit messages |
| Coordinating work schedules and tasks | Sharing confidential data outside approved channels |
| Limited personal use during breaks | Streaming large video files unrelated to work all day |
| Accessing reputable, work-related websites | Visiting illegal download sites or engaging in hacking |
2. Security Measures and Safe Email Practices
Email and web use are central to many cyberattacks. A modern policy should incorporate basic security requirements, aligned with recognized best practices.
- Strong password rules: Require long, complex passwords for email and business accounts, prohibit reuse across services, and encourage passphrases that are easier to remember but harder to guess.
- Multi-factor authentication (MFA): Mandate MFA for company email and key systems where available to make it much harder for attackers to compromise accounts.
- Safe handling of attachments and links: Instruct employees not to open unexpected attachments or click unfamiliar links, especially in messages that are urgent, poorly written, or request sensitive information.
- Use of secure networks: Discourage checking work email or accessing business systems on public Wi-Fi. If remote access is necessary, require use of a virtual private network (VPN) or another secure method to encrypt traffic.
- Reporting suspicious messages: Include a simple procedure for employees to report suspected phishing emails or other unusual activity to the person or team responsible for IT or security.
3. Privacy, Monitoring, and Ownership
Employees need to understand how much privacy they can expect when using company systems and how the business may review data if needed.
- System ownership: Clarify that email accounts, files stored on company devices, and logs of internet activity are company property and may be accessed for legitimate business reasons.
- Monitoring practices: Explain that the business may monitor email and internet use to check for compliance, address security concerns, and meet legal obligations. State that monitoring will be limited to appropriate purposes, not conducted arbitrarily or for unrelated personal reasons.
- Confidentiality and privileged communications: If your business handles sensitive information (such as financial, health, or legal data), require employees to label confidential or privileged messages appropriately and use secure methods where needed.
4. Data Retention and Record Keeping
Businesses increasingly depend on email records for contracts, customer issues, and compliance. At the same time, storing everything forever can be risky and expensive.
- Retention periods: Set a general timeframe for retaining routine emails (e.g., a certain number of years) and designate longer retention for messages related to contracts, regulatory compliance, or ongoing disputes.
- Archiving versus deletion: Explain when messages should be archived, when they may be deleted, and which categories of emails must be preserved.
- Legal holds: Outline how retention rules change when you are notified of a potential legal claim or investigation, including suspension of routine deletion.
5. Use of Social Media, Cloud Tools, and Personal Devices
Your policy should address newer forms of online communication and access. This may be handled in one document or referenced from related policies (such as a bring-your-own-device policy).
- Social media conduct: If employees mention the business online, require them to avoid sharing confidential information, misrepresenting the company, or posting offensive content that could be linked to their role.
- Cloud services: Require use of approved storage and collaboration tools for business data and discourage saving work files to unapproved personal accounts.
- Personal devices: If staff can check company email on personal phones or laptops, specify security requirements (screen locks, updates, and no sharing of devices with unauthorized users) and how access will be revoked if they leave.
Building a Policy That Actually Works
Many policies fail not because of their content, but because they are difficult to understand or never discussed with staff. For a small business, the most effective policy is one that employees can read in a single sitting and apply immediately.
Keep the language clear and practical
- Use plain language instead of legal jargon wherever possible.
- Include brief examples to show what is allowed and what is not, especially for gray areas.
- Organize the policy with headings and bullet points so employees can quickly find sections on topics like security, monitoring, or personal use.
Align with laws and industry standards
The details of your policy should align with relevant laws, regulations, and norms for your sector. For instance, organizations handling health or financial data may have specific confidentiality requirements. Government and cybersecurity guidance on email security and acceptable use can help inform your standards and demonstrate reasonable care.
Integrate training and enforcement
- Onboarding: Review the policy during orientation for new employees and ask them to provide written acknowledgment.
- Regular refreshers: Offer short, periodic training on topics such as phishing, safe browsing, and appropriate communication tone so the rules stay top of mind.
- Consistent enforcement: Apply consequences fairly when rules are violated and document steps taken, especially for serious incidents.
Review and update regularly
Technology, threats, and laws change over time. Update your email and internet policy on a routine schedule, such as once a year, to reflect new tools, security practices, and legal developments.
Practical Clauses to Consider Including
Although every business is different, many small firms find the following types of clauses helpful. You can adapt them to your size, industry, and jurisdiction.
- Scope statement: Clarify that the policy applies to all employees, contractors, interns, and anyone using company systems.
- Ownership and access clause: Confirm that the business owns the email accounts and data stored on its systems.
- Acceptable use clause: Outline what kinds of business and limited personal uses are permitted.
- Prohibited conduct clause: List examples of misuse such as harassment, disclosure of trade secrets, and accessing unlawful content.
- Security clause: Require strong passwords, MFA, secure networks, timely reporting of suspicious messages, and compliance with other security measures adopted by the business.
- Monitoring clause: Inform employees that the company may monitor email and internet activity consistent with the law and for legitimate business purposes.
- Data retention and deletion clause: Set expectations for how long emails and logs are retained and who controls archiving.
- Consequences clause: Explain that violations may result in disciplinary action, up to and including termination, and potential legal action where appropriate.
FAQs: Email & Internet Policies for Small Businesses
Do very small teams still need a written email and internet policy?
Yes. Even if you have only a few employees, a written policy provides clarity and reduces the risk of disputes later. As soon as workers use company accounts or devices, you benefit from documented rules that explain acceptable use, security expectations, and privacy boundaries.
Can I completely ban personal use of email and internet at work?
You can, but many businesses choose not to. A total ban can be difficult to enforce and may harm morale. Instead, many employers allow limited personal use that does not interfere with work, violate laws, or compromise security, while clearly defining what is off limits.
Do employees have a right to privacy in work email?
Expectations vary by jurisdiction, but generally employees should not assume full privacy in work-provided accounts. To avoid misunderstandings, your policy should clearly explain that systems are company property and may be monitored for legitimate business reasons, subject to applicable law.
How often should I update my policy?
Review your email and internet policy at least annually or whenever you introduce new systems, face new security threats, or see changes in relevant laws or regulations. Regular updates show you are taking reasonable steps to respond to evolving risks.
Is an email policy enough to protect against cyberattacks?
A policy by itself is not enough, but it is an important piece of a broader cybersecurity program. You should also invest in technical protections such as secure email gateways, anti-malware tools, domain authentication, and regular patching, combined with ongoing employee training.
References
- Email security best practices (ITSM.60.002) — Government of Canada, Canadian Centre for Cyber Security. 2023-03-01. https://www.cyber.gc.ca/en/guidance/email-security-best-practices-itsm60002
- Top 11 Email Security Best Practices for Businesses — Rippling. 2025-01-15. https://www.rippling.com/blog/email-security-best-practices
- Cyber Security Best Practices for Small Businesses — Storable. 2023-08-10. https://www.storable.com/resources/cyber-security-best-practices-for-small-businesses/
- Emails in the workplace: 5 best practices for businesses and employers — Chenoweth Law Group. 2021-04-19. https://www.chenowethlaw.com/blog/2021/04/emails-in-the-workplace-5-best-practices-for-businesses-and-employers/
- ePolicy Best Practices — The ePolicy Institute. 2014-01-01. http://www.epolicyinstitute.com/docs/ePolicyInstitute~ML~EmailBestPractices.pdf
Similar Articles








Read full bio of medha deb


