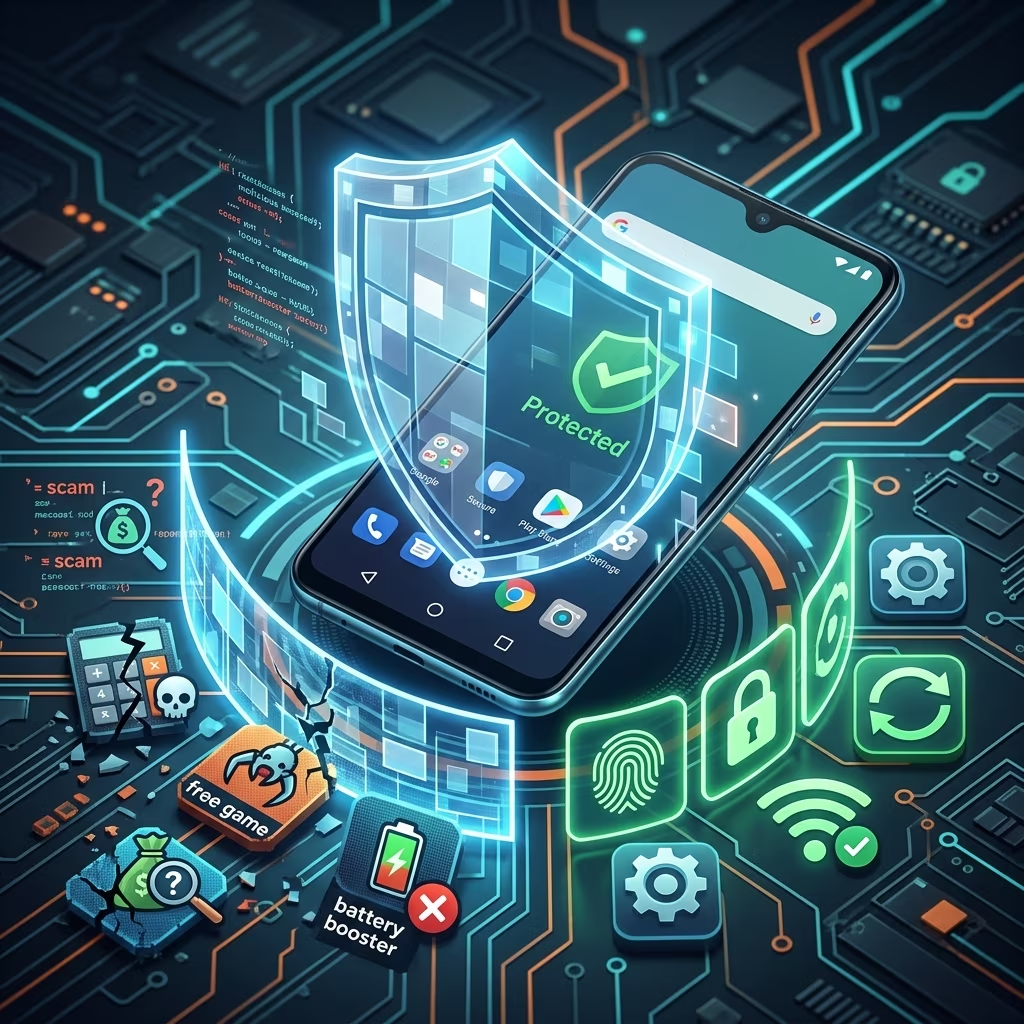
Android has become the most widely used mobile operating system in the world, which makes it a prime target for cybercriminals who hide malicious apps and scams in plain sight. Fake utilities, streaming tools, banking apps, and even news readers can quietly drain your money, steal your passwords, or take over your phone if you are not careful.
This guide explains how Android malware apps work, the scam tactics attackers commonly use, and the concrete steps you can take to protect your device, your accounts, and your mobile bill. It is inspired by legal and consumer warnings about Android app scams but written entirely in original language with additional technical detail and practical advice.
Why Android Is a Prime Target for Malware Apps
Cybercriminals focus heavily on Android for several reasons: its global market share, the diversity of devices and manufacturers, and the flexibility of installing apps from multiple sources (official stores and third-party sites). This flexibility benefits power users and developers, but it also opens the door to malicious apps that bypass built-in protections.
- Huge user base: A single malware campaign can reach millions of devices, making Android attractive for organized crime and fraud networks.
- Sideloading and third-party stores: Unlike some closed ecosystems, Android allows users to install apps from outside the official Google Play Store, which attackers exploit to distribute fake apps and spyware.
- Permission model: Many legitimate Android apps need broad permissions (access to SMS, storage, camera, or Accessibility services), giving malware authors an excuse to ask for the same powerful controls.
When users are rushed, distracted, or tempted by a free offer, they may grant permissions or install apps they barely examine, giving attackers direct access to sensitive data and powerful control over the device.
Common Types of Malicious Android Apps
Not all malware behaves the same way. Understanding key categories helps you spot unusual activity faster and react appropriately. Google Play Protect uses specific classifications to describe harmful behavior in Android apps.
| Malware Type | Main Goal | Typical Symptoms |
|---|---|---|
| Billing fraud | Secretly charge users via carrier billing or premium services | Unexplained subscription charges on mobile bills; SMS to premium numbers |
| Spyware | Monitor activity and steal data, messages, or files | Higher data usage, strange permissions, possible performance slowdown |
| Trojans / hostile downloaders | Appear harmless but download or execute harmful code | Random pop‑ups, installation of other apps, intrusive ads |
| Credential stealers | Capture login details and financial information | Fake login screens, suspicious banking prompts, password theft |
| Ad fraud apps | Generate fake ad views or clicks to make money | Battery drain, background network activity, device overheating |
Malicious apps frequently combine several of these behaviors. For example, one campaign may use a Trojan disguised as a utility app that secretly performs billing fraud and steals credentials at the same time.
How Android Malware Apps Spread
Attackers need you to install their app before they can do harm. Modern Android malware relies on social engineering and technical tricks to get onto your phone.
1. Fake apps and brand impersonation
Many campaigns revolve around apps that pretend to be legitimate tools—such as banking apps, secure messaging plugins, news readers, streaming tools, or even government ID apps.
- Malicious apps copy names, icons, and descriptions of well-known services.
- Deceptive websites or messages claim the app is an “upgrade” or “pro version” not yet available in the official store.
- Users are told to download an APK file directly and enable installs from “unknown sources,” bypassing normal protections.
2. Sideloaded APKs from untrusted sources
One of the most straightforward infection methods is convincing users to manually install APK files from third-party sites, chat groups, or forums.
- Suspicious links in SMS, messaging apps, or social media invite you to install a “must-have” app.
- Unofficial streaming or download sites may embed malware into their “download app” buttons.
- Romance scams and fake communities sometimes require installing a “special chat app” to continue talking.
3. Abuse of Accessibility and advanced permissions
Once installed, many malware apps request powerful permissions that go far beyond what is necessary for their supposed features. Some target Accessibility services, which can give them the ability to read the screen, tap buttons, and control the device remotely.
- Requests to control Accessibility services, notifications, or install other apps are strong warning signs.
- With these permissions, attackers can approve their own pop-ups, intercept one-time passcodes, and manipulate banking apps.
Real-World Scam Patterns Targeting Android Users
Recent security research has identified multiple real-world Android campaigns that show how far attackers are willing to go to monetize malicious apps.
- Carrier billing fraud: A long-running campaign used hundreds of fake apps to silently subscribe users to premium services, targeting specific mobile operators and countries.
- Spyware disguised as privacy tools: Attackers created fake versions of encrypted messaging plugins and chat apps; once installed, the spyware exfiltrated files and device data.
- Romance scam chat apps: In some cases, scammers lured victims into installing a malicious chat app that was never available through official stores, leading to data theft and account compromise.
- Ad-fraud and credential theft blends: Certain malicious APKs use the device to generate fake ad traffic while simultaneously stealing login details.
- AI-assisted banking malware: Newly discovered malware has abused generative AI to analyze screen activity and remotely control devices, especially around financial apps.
These campaigns demonstrate that Android malware is not just about annoying ads; it can directly impact your finances, privacy, and personal safety.
Warning Signs Your Android Device May Be Infected
Detecting malware early can significantly reduce harm. Google and security vendors highlight several signs that may indicate your device hosts unsafe software.
- Unexpected pop-ups or redirects: Frequent full-screen ads, browser tabs opening on their own, or redirections to suspicious sites.
- Unusual charges: New premium service subscriptions or charges on your mobile bill that you do not recognize.
- Performance and battery issues: Sudden battery drain, overheating, or slow performance due to background activity.
- Permissions that do not match the app’s purpose: Apps asking for control of SMS, Accessibility, notifications, or installation of other apps for simple features.
- Account security alerts: Automatic sign-outs, login warnings, or alerts from Google or your bank about suspicious activity.
Any one of these signs does not confirm malware, but multiple symptoms together—especially after installing a new app from an untrusted source—should prompt immediate action.
Core Strategies to Prevent Android Malware Infections
The most effective defense against Android malware is to avoid installing malicious apps in the first place. Combining official security tools with careful user behavior dramatically reduces your risk.
1. Stick to trusted app sources
Security experts consistently recommend downloading apps only from official stores or the verified provider’s website.
- Prefer the Google Play Store for Android apps; its review and automated scanning processes block many known threats.
- Avoid APKs sent via messages, forums, or unofficial streaming sites, especially if they require enabling “unknown sources.”
- For specialized apps (banking, government ID, health providers), cross-check that the app is linked from the official organization’s site.
2. Audit app permissions before and after install
Carefully reading and managing app permissions is one of the best ways to prevent abuse.
- Ask yourself whether an app truly needs each permission it requests—especially access to SMS, call logs, Accessibility services, or the ability to install other apps.
- Deny or revoke permissions that seem unrelated to the app’s core function.
- Regularly review installed apps and their permissions in your device settings and uninstall those you do not recognize or trust.
3. Keep Android and apps up to date
Updates often contain security patches that fix vulnerabilities exploited by malware.
- Enable automatic updates for both Android system software and apps from the Play Store.
- Periodically check for security updates in your device’s “Security & privacy” or “System & updates” settings.
- Restart your phone after updates to ensure patches are applied correctly.
4. Use Google Play Protect and security tools
Google Play Protect is built into Android and automatically scans apps for harmful behavior. It classifies malware types (such as backdoors, billing fraud, stalkerware, spyware, and trojans) and warns or removes apps that pose risk.
- Open the Google Play Store, go to your profile, and confirm that Play Protect scanning is turned on.
- Run manual scans if you have recently installed apps from unfamiliar developers.
- Consider an additional reputable mobile security app that offers real-time scanning and fraud warnings.
5. Be skeptical of urgent or emotional messages
Many malware campaigns begin with a message or pop-up designed to provoke immediate action, such as fear or desire.
- Ignore links claiming you must “update immediately” by installing an APK outside the official store.
- Be cautious about chat invitations that require installing a separate app, especially in romance or investment contexts.
- Verify unusual warnings by visiting official sites or contacting providers directly, rather than trusting unsolicited messages.
What To Do If You Suspect Your Android Phone Has Malware
If you think you have installed a malicious app, acting quickly can help reduce damage and keep your accounts safer.
Immediate steps
- Disconnect from networks: Turn on airplane mode and temporarily disable Wi‑Fi to limit data exfiltration.
- Identify recent installs: Check your app list for anything installed shortly before problems began; uninstall apps you do not trust or recognize.
- Run malware scans: Use Google Play Protect and any installed security app to scan for harmful software.
Protect your accounts and finances
- Review your bank, payment, and government accounts for unauthorized transactions and unusual login activity.
- Change passwords for key accounts, especially email, banking, and social media, using a trusted device.
- Monitor your mobile carrier bill for new subscriptions or premium charges you did not authorize.
Reset and seek help if necessary
If signs of infection persist or if critical accounts have been compromised, stronger measures may be necessary.
- Perform a factory reset after backing up essential data, to remove persistent malware.
- Contact your mobile carrier regarding suspicious charges and ask about blocking premium services.
- Report confirmed fraud to your bank, relevant authorities, and local law enforcement.
- If you are unsure how to proceed, consult the device manufacturer’s support or a professional technician.
Frequently Asked Questions About Android Malware Apps
1. Is every app outside Google Play automatically dangerous?
No. Some legitimate developers distribute apps directly, and enterprise environments may use internal app distribution. However, the risk is significantly higher with third-party sources because they lack the same automated scanning and policy enforcement as Google Play. Only install external apps if you can verify the developer’s identity and trust the source.
2. Can malware survive a factory reset?
Most typical Android malware is removed when you perform a full factory reset, which wipes user data and installed apps. Very rare, highly sophisticated threats might attempt to exploit firmware or root-level access, but those cases are exceptional. For the vast majority of consumer infections, a reset is an effective last resort.
3. Do I need an additional security app if I already have Play Protect?
Google Play Protect provides a strong baseline by scanning apps and blocking known harmful behavior. A reputable third-party security suite can add features such as phishing protection, enhanced web filtering, or more detailed malware detection. Whether you need one depends on your risk tolerance and usage habits, but combining cautious behavior with built-in protections is essential.
4. Can clicking a pop-up alone infect my Android phone?
Simply viewing or dismissing a pop-up or visiting a website usually is not enough to install malware on a modern, fully patched Android device. In most cases, infection requires you to install an app or grant specific permissions. However, some malicious sites may attempt browser-based attacks or trick you into enabling harmful settings, so it is always wise to close suspicious pages and avoid downloading anything they offer.
5. How often should I review my installed apps?
Reviewing your installed apps every few weeks is a good habit, especially if you frequently try new tools. Uninstall apps you no longer use, remove those from unknown developers, and re-check permissions for apps that handle sensitive data or communications.
Key Takeaways for Safer Android Use
- Use official stores like Google Play and avoid random APK downloads.
- Scrutinize app permissions and deny access that is not clearly necessary.
- Keep your device and apps updated and ensure Play Protect is active.
- Watch for unusual charges, performance issues, and security alerts.
- Act quickly—uninstall suspicious apps, run scans, and protect your accounts if you suspect a problem.
By combining technical defenses with mindful habits, you can significantly reduce your risk of falling victim to Android malware apps and scams—and keep your personal data and finances safer.
References
- Unmasking Malicious APKs: Android Malware Blending Click Fraud and Credential Theft — LevelBlue SpiderLabs. 2024-10-01. https://www.levelblue.com/blogs/spiderlabs-blog/unmasking-malicious-apks-android-malware-blending-click-fraud-and-credential-theft
- “Sneaky” new Android malware takes over your phone, hiding in fake news and ID apps — Malwarebytes Labs. 2025-11-18. https://www.malwarebytes.com/blog/news/2025/11/sneaky-new-android-malware-takes-over-your-phone-hiding-in-fake-news-and-id-apps
- Android Malware Used Fake Apps to Charge Users in Mass Billing Fraud Campaign — Infosecurity Magazine. 2023-09-28. https://www.infosecurity-magazine.com/news/android-carrier-billing-fraud-four/
- Android malware in the wild: 18 real campaigns discovered by ESET — ESET. 2026-02-20. https://www.eset.com/blog/en/home-topics/cybersecurity-protection/cybercriminals-targeting-android-os-are-getting-creative/
- Malware | Play Protect — Google for Developers. 2024-06-10. https://developers.google.com/android/play-protect/phacategories
- Remove malware or unsafe software – Android — Google Account Help. 2024-05-15. https://support.google.com/accounts/answer/9924802
- How you can protect your phone from Android malware scams — YouTube / Google Singapore. 2023-08-15. https://www.youtube.com/watch?v=N1kVZRuvrtg